Scan Python locally
Scan a file or folder for selected SQL and shell command patterns. Isolated workers apply limits and let the reviewer cancel a scan.
Prototype in development
We’re developing NEXIRYN Evidence for small software teams and consultants who hand over security findings to clients or project reviewers.
The available prototype scans locally for selected patterns in Python code, records review decisions and exports an HTML report. Support for release documents and SBOMs is planned.
Scan a file or folder for selected SQL and shell command patterns. Isolated workers apply limits and let the reviewer cancel a scan.
Reopen validated JSON from project history, mark findings as reviewed and choose whether to include notes in an export.
Compare two saved scans and export a project review in English or Polish. The standalone HTML opens offline in a browser.
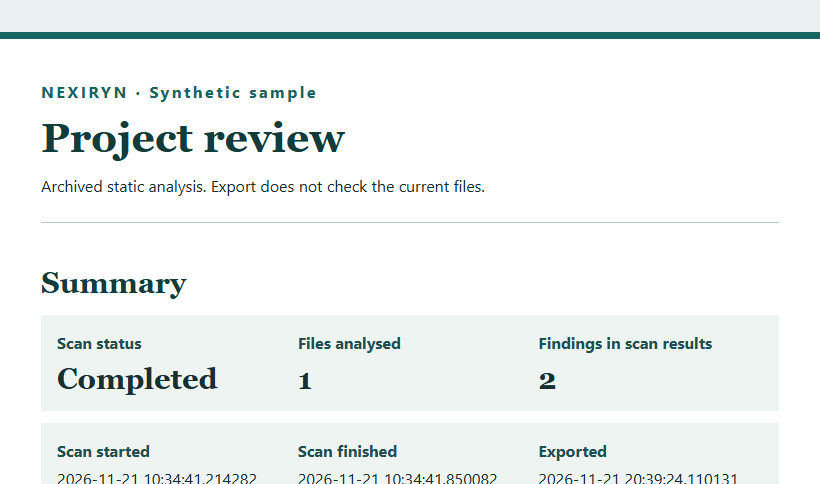
NEXIRYN generated this report after scanning one synthetic Python file.
In fixture.py, the scanner flagged SQL001 on line 6 and CMD001 on line 7, both at column 20.
The “User decision” field shows “Reviewed” for SQL001 and “No data” for CMD001.
“Analysis scope” covers one file checked with SQL001 and CMD001, and the export does not verify its current contents.
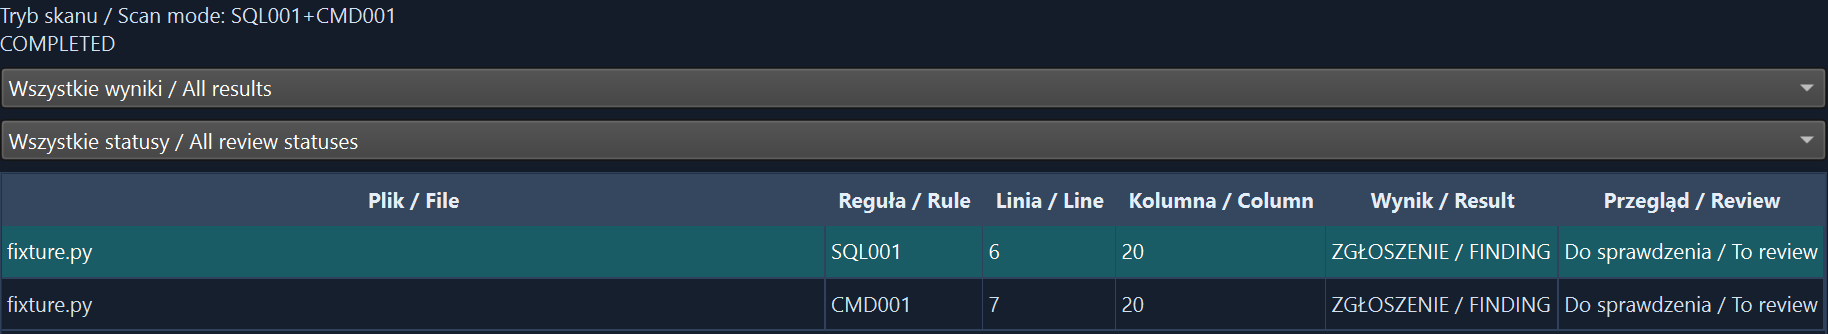
The results table keeps each rule and its location visible.
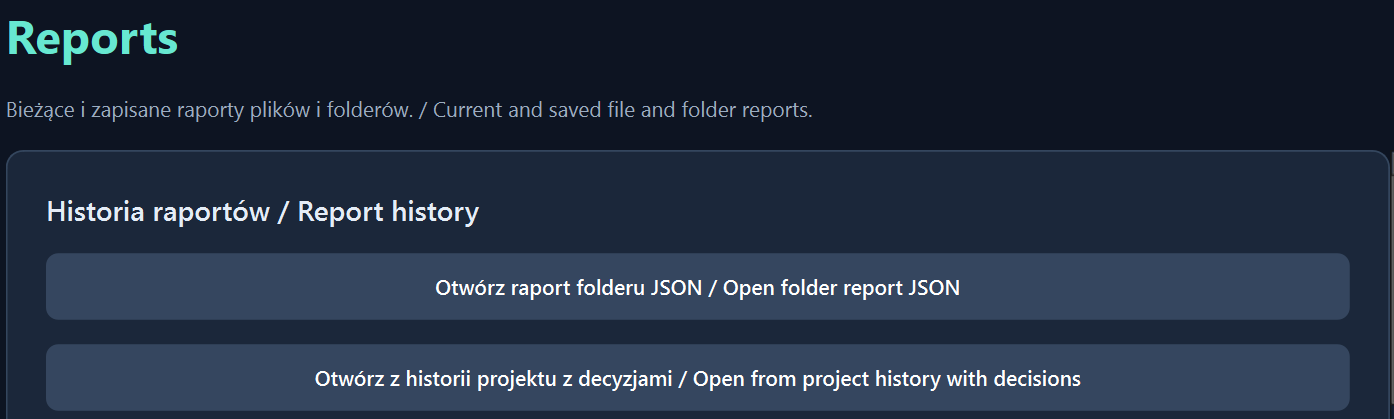
The Reports view can reopen project history together with its review decisions.
42bb4e4The desktop app scans Python files locally and exports project reviews. Release checks and SBOM import are planned for NEXIRYN Evidence.
Download prototypeNEXIRYN-Windows-x64-42bb4e4.zip0f6ebcb4fd63b1be7ea84733bca6ece44e3ff5935a598062babc5738acfafe87START.txt lists the older commit cdbfee2 by mistake. ENVIRONMENT.json and the verified contents of the application modules confirm that this package is version 42bb4e4.
Start-NEXIRYN.cmd.examples/combined_scan_demo.py and click Scan file. Use the example as scan input only.The ZIP includes CPython 3.12.10 and Qt. Scans run offline; reports and history use your Windows profile. Optional AI chat requires a separate local Ollama installation and model.
Expect two findings, one SQL001 and one CMD001. Each flags a pattern for human review. Other vulnerabilities may go undetected.
Send feedback to [email protected].
The next prototype would associate a product and release with existing documents, import one SBOM format and check selected relationships for consistency.
A release review would distinguish tool findings, supplier declarations, discrepancies, missing information and human decisions.
NEXIRYN is an independent development project. Its author is preparing the local prototype for feedback from software teams and security consultants.
The current review records a static scan. A SHA-256 match checks bytes against a supplied digest. Authorship, test execution and the link to a shipped binary each need separate evidence.